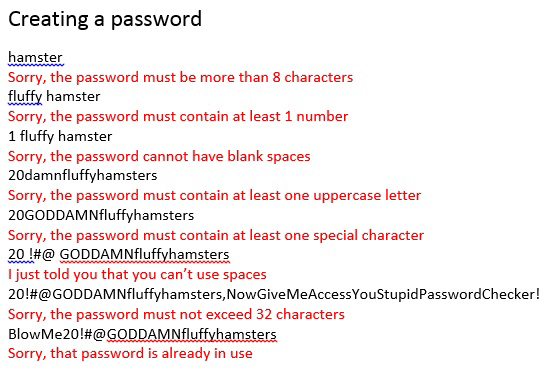
Obligatory https://neal.fun/password-game/
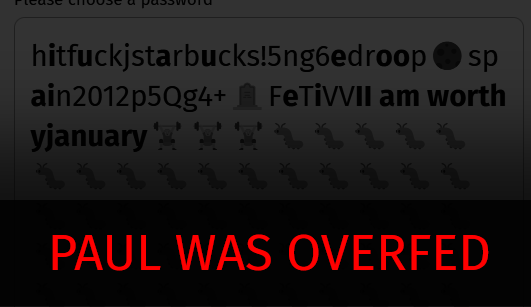
Well, that’ll teach you to actually take care of your pets and not just dump their food in front of them and be done with it.
(fuck paul tho fr)
I closed my laptop when it asked for the Wordle of the day.
Enter the same thing 5 times and you’re good for the day :)
This game made me so angry haha
Infuriating fact: if a service has maximum password length limits (lower than 1000 characters), they’re reversibly storing your password and if they’re that lazy it’s probably plain text
Couldn’t it just be that they’re using something like bcrypt which won’t take any chars above its limit into account (knowing that there’s a limit will pretty much never matter to a user but why obscure the fact)? What does it even mean to store it reversibly, just because they have a char limit doesn’t mean they are encrypting the password, could just be some frontend shenannigans as well.
They may just base their limit on one or a few block sizes of the hash function.
That sounds incredibly unlikely. I would be good money that 99% of password length limits are not based on concrete limits. Things like “100 should be enough 🤷” must be way more common.
I doubt 1% of programmers are away of their hashes block size. It is also probably irrelevant since after the first round everything is fixed size anyways.
Nope. No point in storing > 256 or even 128 chars for a password anyway. Useless storage wasted. Also it doesn’t really mean they store the password badly in the server.
Ok but are 15 characters too much?
I’ve seen 14-char limits, which are NOT reasonable
Ignoring that they must be hashed to be acceptable and that it’s not possible for 1000 characters of text to add up to a waste of storage worth mentioning in pretty much any environment, it’s literally impossible for a 128 character password limit to be beneficial in any way.
A limit below that demonstrably lowers security by a huge margin.
Fun fact: Lemmy instances cap at 60. they’re not storing reversibly, they’re just using bcrypt and rather than pre-hashing the pw before bcrypt like most bcrypt users do, they just truncate to 60.
60 makes sense, 14 does not
I don’t get why some sites limit your usage of special characters and have miniscule max lengths?? looking at you PayPal you piece of shit
“This password would take 1 century to crack!”
There was a website where I was making an account and it was like: no semicolons.
To this day I wonder if that was how they blocked sql injection.
Escaping by obstruction ^^
deleted by creator
The only security threat would be the site itself. How do they know other users have the same password?
Options:
-
They have your password in plain text in their DB. CHEFF KISS
-
They aren’t using salts.
-
They are using the same salt for everyone.
All of them concerning.
-
The right answer is use a password manager to generate and store a long password. Then it doesn’t matter.
If for some reason you want a secure password and aren’t using a password manager https://www.grc.com/passwords.htm
Does anyone use the generator from chrome anymore? Like a 2023 password for me is “suggest strong password”…
Fuck that shit, just give me the password